QIR Role Access and Security
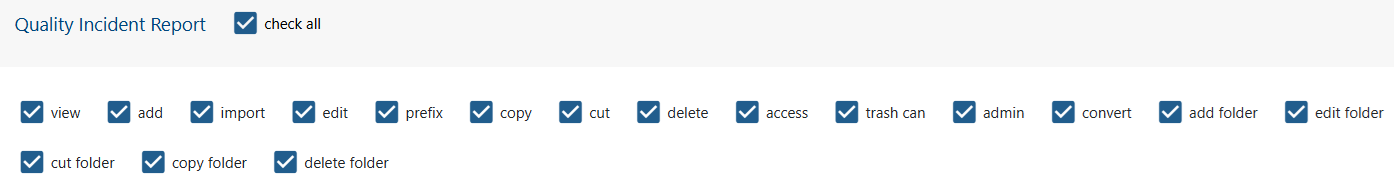
Access to the QIR Module and its functionality is controlled by a set of role permissions defined within the Role Management module of each project. These permissions include:
view - protects access to one or many QIRs.
add - protects ability to add a new QIRs.
import - protects ability to add files to QIRs.
edit - protects ability to edit QIRs data.
prefix - protects ability to change folder prefix storing QIRs.
copy - protects ability to duplicate QIRs.
cut - protects ability to move QIRs.
delete - protects ability to move QIRs to the trash can.
access - protects ability to change QIRs folder access.
trash can - protects ability to permanently remove QIRs from a designated trash can.
admin - protects ability to perform any kind of actions, after QIRs has been closed.
convert - protects ability to convert a new QIRs report to a NCR.
add folder - protects ability to add a new QIRs folder.
edit folder - protects ability to edit QIRs folder data.
cut folder - protects ability to move QIRs folders.
copy folder - protects ability to copy QIRs folders.
delete folder - protects ability to move QIRs folders to the trash can.
Additionally, the system audit tracks each time a Submittal is:
Viewed
Updated
Added
Deleted
The audit log records who performed the action, what was done, and when the interaction occurred.